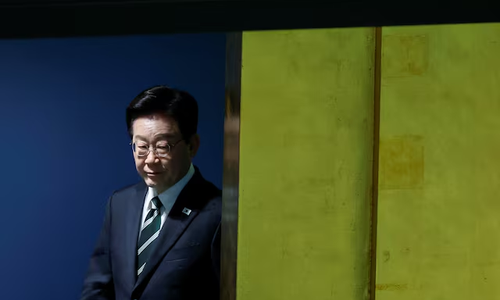
South Korea is dealing with one of its worrying cybersecurity episodes in the financial sector in recent memory. President Lee Jae Myung has ordered an investigation and a coordinated response to a string of personal data leaks. The incidents have affected banks, finance companies and public agencies. Seouls presidential office confirmed the order on Sunday, October 4.
What makes this story significant is not the number of institutions involved. Regulators now suspect the attackers were not chasing one target. They may have been probing the financial system at once looking for the weakest door.
What. How it unfolded?
The timeline shows how quickly the situation grew.
Shinhan Bank reported a breach on September 30. The Financial Services Commission (FSC) the countrys financial regulator responded by launching on-site investigations. Within days the picture widened. On Friday, October 2 the FSC held an emergency meeting. Said that Shinhan Bank, KB Kookmin Bank and other lenders had reported cyberattacks. Separately Yonhap news agency reported that Hana Bank and Woori Bank had also suffered breaches. That means all four of the countrys best‑known banks have now been named in connection with the incidents.
Then the problem spread further down the industry. According to Korean media reports additional breaches were found at second‑tier financial institutions. That discovery pushed regulators to move their emergency meeting forward from October 7 to Sunday, October 4.
At the time of reporting the banks could not be reached for comment as it was outside working hours. No institution had yet given an account of what data was exposed or how many customers are affected. This is a gap and readers should treat any specific numbers circulating online with caution until the banks or regulators confirm them.
The governments response
FSC Chairman Lee Eog‑weon convened Sundays meeting with financial industry associations, regulators and executives from the institutions. His message was blunt: the sector must respond with the level of vigilance.
The regulator gave institutions a clear set of instructions:
- Carry out comprehensive security inspections of their systems.
- Tighten access controls.
- Minimise external access to systems.
- Strengthen protections for consumers.
The FSC also said that attack methods, internet protocol (IP) addresses and other threat intelligence will be shared rapidly across the industry. This matters more than it may sound. Hackers often reuse the techniques and infrastructure against multiple targets. If one bank spots a pattern and warns the others within hours than days the next attack has a much smaller chance of succeeding.
The AI question
One of the notable parts of the FSC chairmans remarks was about artificial intelligence. Lee said authorities cannot rule out that AI was used in the attacks. He called for an approach summed up as “AI attacks defended by AI”. Signalled that broader upgrades to the financial sectors cybersecurity framework are coming.
It is worth being careful. The regulator said it cannot rule out AI involvement. That is not the same as confirming it. No evidence has been made public showing that AI tools were used. Still the comment tells us how seriously officials take the direction of the threat. Automated tools can scan thousands of systems for weaknesses faster than a human team can and defenders are increasingly expected to use similar automation to keep pace.
Scanning, not a strike
According to Yonhap regulators believe the attacks may have broadly scanned multiple financial companies for vulnerabilities rather than targeting one institution in particular. Think of it as someone trying the handles on every car in a parking lot of breaking into one specific vehicle.
This kind of pattern has an implication. Even institutions that have not yet reported a breach could be exposed, which explains why the FSC ordered security inspections across the sector of only at the banks already named.
Where did the attack traffic come from?
Yonhap citing bank data submitted to lawmakers reported that the attack traffic came from IP addresses in countries, including the United States, Japan, Singapore, Vietnam and Britain.
Readers should not over‑read this. An IP address shows where traffic passed through not necessarily where the attacker is sitting. Hackers routinely route their activity through servers in countries to hide their identity. A list of countries on its own does not tell us who is, behind the attacks.
The political angle: North Korea
The political reaction has already begun. South Koreas main opposition People Power Party has said that authorities should also investigate whether North Korea was involved. The party has pointed to cyberattacks on South Korean financial institutions that have been attributed to Pyongyang.
This is a call for investigation, not a finding. No official source has linked the incidents to North Korea and investigators have not announced any attribution. In cases attribution usually takes weeks or months of forensic work and governments tend to be cautious before naming a state actor publicly. It is fair for the opposition to ask the question. Readers should not treat it as an established fact.
Why this matters beyond South Korea?
Banks are among the well protected organisations in any economy. When several of them report breaches within days of each other it raises questions about how well the wider financial system can withstand coordinated pressure.
There are three reasons this story deserves attention.
First, scale and speed. The incidents moved from one bank to four banks and then to smaller institutions in barely a few days. That shows an attacker or a group of attackers working systematically.
Second the data at stake. Personal data from institutions can include names, contact details and account information. Even when money is not stolen directly this data can be used later for phishing, impersonation and fraud. The harm often appears weeks or months after the breach.
Third trust. Banking runs on confidence. Customers need to believe their information is safe. How quickly and honestly the banks and regulators communicate over the coming days will matter as much as the technical fix.
What customers can do now?
The banks have not yet confirmed what was exposed. It is best to act carefully without panicking. These are sensible precautions anyone can take after a breach is reported at their bank:
- – Change your passwords for banking apps and any other account where you reuse the same password. Use a password for each service.
- – Turn on two-factor authentication wherever it is offered.
- – Be suspicious of calls, texts and emails that claim to be from your bank. Fraudsters often act quickly after a breach is in the news. Do not click links in messages. Contact the bank through its app or phone number instead.
- – Check your statements and transaction alerts regularly and report anything unfamiliar straight away.
- – Rely on announcements from your bank and the FSC not on social media rumours.
What to watch next?
Several questions remain open. The coming days should bring more clarity:
- Which banks and institutions were affected and exactly what data was exposed?
- How many customers are involved?
- Was the attack coordinated and who is behind it?
- Will the FSC announce binding cybersecurity rules for the sector as the chairman hinted?
- Did the attackers actually use AI tools. Is that still only a possibility?
The government has made clear that this is being treated as a national-level problem. President Lees order to investigate the FSCs emergency meetings and the push, for real-time information sharing all show that officials want to contain the damage and learn from it quickly. Whether the response is fast and transparent enough to rebuild confidence is the real test.